The Federal Hammer Drops
When the White House cybersecurity guidelines dropped in February 2026, mandating memory-safe programming languages for all federal contractors by 2028, the collective groan from legacy C++ shops was audible across Silicon Valley. I’ve watched this industry pivot through framework wars, language adoptions, and architectural revolutions. This feels different.
The mandate isn’t just policy theater. It has teeth. Federal contracts now require explicit memory safety guarantees for critical systems. No more handwaving about “experienced developers” and “mature codebases.” The government wants provable safety, and they’re willing to walk away from vendors who can’t deliver it.
Here’s what’s happening in the trenches. Companies with decades of C++ infrastructure are staring at a choice between massive technical debt migration or losing lucrative government contracts. The math is brutal. Rewriting mission-critical systems isn’t just expensive — it’s existentially risky for organizations built around C++ expertise.
The Numbers Don’t Lie
Microsoft’s January 2026 admission that 67% of their security vulnerabilities between 2019 and 2024 were memory safety issues sent shockwaves through the enterprise world. These aren’t toy applications or weekend projects. This is Windows, Office, Azure — systems that power global infrastructure.
Google’s Chrome team provided even more concrete evidence. Their ongoing Rust migration prevented an estimated 2,847 memory safety vulnerabilities in 2025 alone, translating to $12 million in avoided security incident response costs. That’s not hypothetical ROI. That’s money staying in the bank instead of flowing to incident response teams and legal departments.
The Rust Foundation Annual Report 2025 shows enterprise adoption exploded 178% last year. Dropbox, Meta, and Figma have migrated performance-critical services. These aren’t companies known for chasing trends. They’re data-driven organizations that moved when the business case became undeniable.
The Talent Hemorrhage
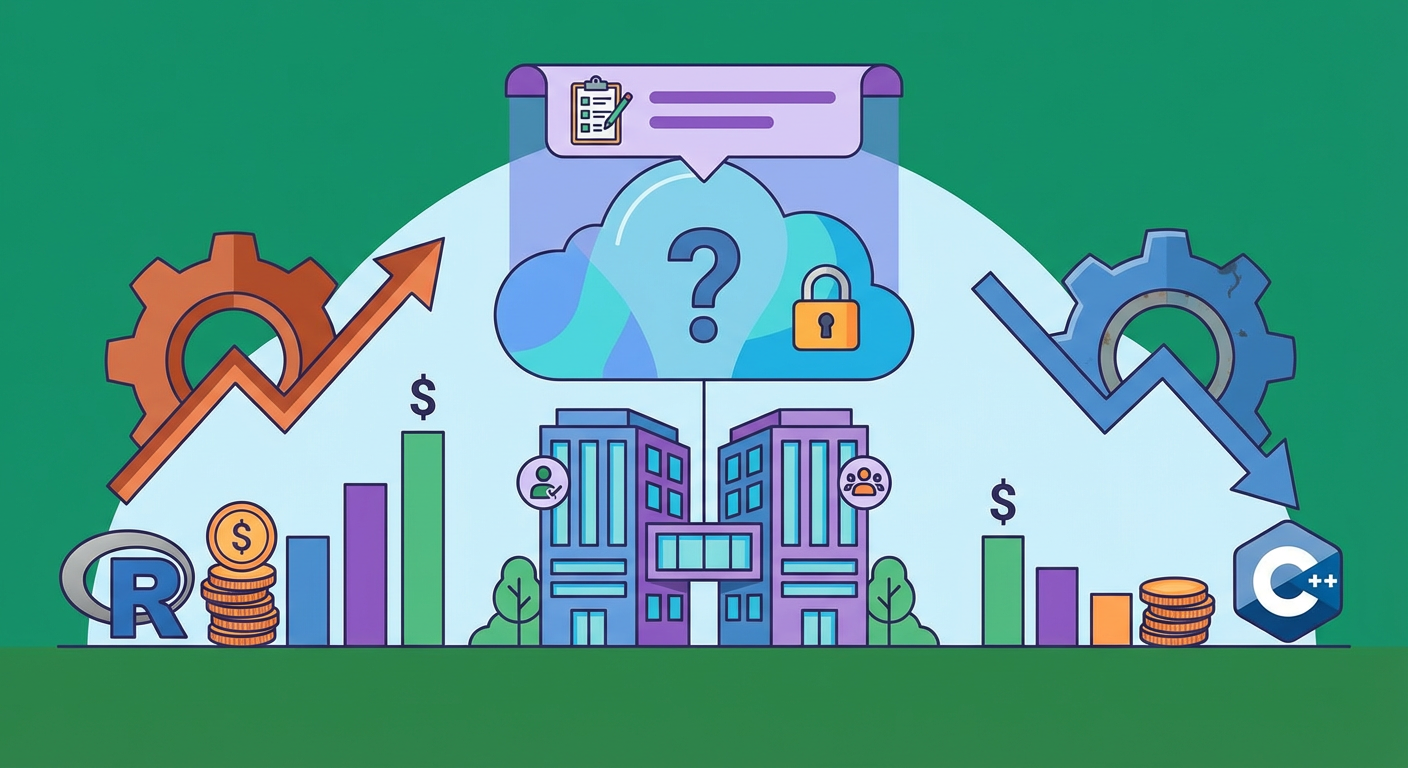
Stack Overflow’s 2025 survey revealed something that should terrify C++ shops: Rust developers now command an average salary of $97,000 compared to $89,000 for C++ developers. That $8,000 gap represents a fundamental market shift. The premium isn’t just about scarcity — it’s about value.
I’ve seen this pattern before. When mobile development took off, iOS and Android developers commanded premiums while desktop developers watched their market value stagnate. The difference here is speed. The mobile transition took a decade. The memory safety transition is happening in quarters, not years.
Legacy shops are caught in a vice. Their senior C++ developers are either retiring or pivoting to Rust. Junior developers are learning Rust first, treating C++ as legacy knowledge. The pipeline is drying up from both ends. Companies that spent decades building C++ expertise are watching that investment evaporate in real time.
Technical Reality Check
Let’s be honest about what migration actually means. You can’t just recompile C++ code in Rust and call it done. Memory management patterns that worked for decades in C++ become compilation errors in Rust. Pointer arithmetic disappears. Manual memory management gets replaced by ownership semantics that fundamentally change how you structure programs.
The good news is that Rust’s safety guarantees are real. Use-after-free bugs, buffer overflows, and double-free errors become impossible by design. The bad news is that “impossible by design” means your existing C++ patterns won’t compile. You’re not just changing languages — you’re changing how you think about data flow and ownership.
I’ve guided three different migration projects in the last eighteen months. The teams that succeeded treated it as a greenfield rewrite with C++ as a specification reference. The teams that tried to port line-by-line burned months fighting the borrow checker before finally admitting they needed to start over.
The Path Forward
The federal mandate isn’t going away. The technical evidence isn’t disappearing. The talent pipeline isn’t reversing. Legacy C++ shops need to accept that the question isn’t whether to migrate, but how quickly they can do it without destroying their existing business.
Smart organizations are starting with new features and greenfield components. They’re using Foreign Function Interface (FFI) to maintain interoperability while gradually expanding Rust’s footprint. The approach requires discipline, but it’s less risky than big-bang rewrites.
The companies that will survive this transition are those that start planning now, not in 2027 when the deadline looms. They’re investing in Rust training for their existing teams while hiring new Rust developers. They’re identifying which systems absolutely must migrate for compliance and which can remain in maintenance mode.
I’ve seen enough technology transitions to know that fighting market forces is expensive and futile. The memory safety mandate represents more than policy — it’s recognition that decades of C++ security incidents have reached an unacceptable threshold. The question isn’t whether you believe in Rust’s superiority. The question is whether you can adapt quickly enough to keep your contracts and your talent.
