The Federal Hammer Drops When the White House cybersecurity guidelines dropped in February 2026, mandating memory-safe programming languages for all federal contractors by 2028, the collective groan from legacy C++ shops was audible across Silicon Valley. I’ve watched this industry pivot through framework wars, language adoptions, and architectural revolutions. This feels different. The Memory Safety …
Continue reading The Memory Safety Mandate: Why Legacy C++ Shops Are Bleeding Talent and Money
Author:Owen Mitchell
Why Your CI/CD Pipeline Breaks at 3 AM (And How I Learned to Sleep Again)
Three years ago, I got woken up at 2:47 AM by a deployment that decided to push corrupted configuration files to production. The pipeline had passed every test. Green checkmarks across the board. But somewhere between the artifact build and the deployment step, a race condition in our Jenkins setup had allowed a partial file …
Continue reading Why Your CI/CD Pipeline Breaks at 3 AM (And How I Learned to Sleep Again)
Why Your Vulnerability Assessment Is Fighting Yesterday’s War
The CVSS Theater and Its Missing Act I watched a security team spend three weeks prioritizing a CVSS 9.8 vulnerability in a library that hadn’t been loaded in production for two years. Meanwhile, a privilege escalation bug in their custom authentication middleware sat unpatched because it didn’t have a CVE number. This scene plays out …
Continue reading Why Your Vulnerability Assessment Is Fighting Yesterday’s War
Why Go’s Garbage Collector Won’t Save You From Memory Leaks (And What Actually Will)
The 16GB Server That Taught Me Humility Three years ago, I watched a Go service consume 16GB of RAM on what should have been a trivial API endpoint. The garbage collector was running. Memory was being freed. Yet our monitoring showed a steady climb that eventually triggered the OOM killer. The team blamed Docker limits, …
Continue reading Why Go’s Garbage Collector Won’t Save You From Memory Leaks (And What Actually Will)
Rolling Updates Are Not Enough: What Production Kubernetes Really Demands
The Tuesday Morning That Changed Everything Picture this: 3:47 AM Pacific, your largest customer can’t log in, and your “battle-tested” rolling update just took down 60% of your authentication service. The pods are cycling endlessly. Your metrics show green across the board because your health checks are lying to you. This isn’t a hypothetical scenario. …
Continue reading Rolling Updates Are Not Enough: What Production Kubernetes Really Demands
gRPC: The Communication Protocol Your Microservices Actually Need
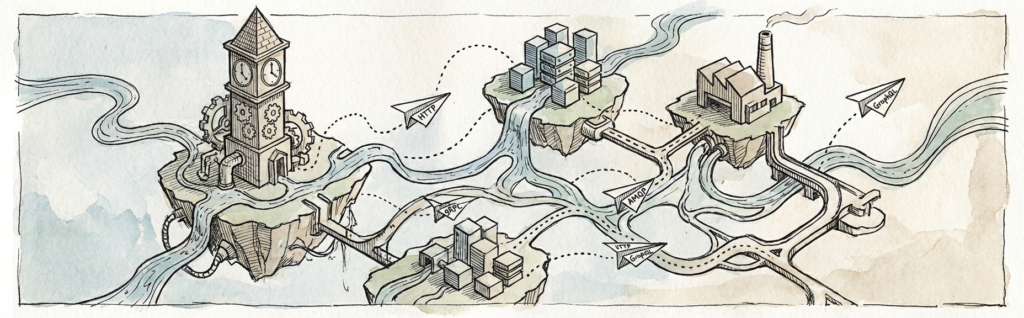
Why Most Teams Get Protocol Selection Wrong Three years ago, I watched a team spend six months debugging intermittent failures in their REST-based microservices architecture. The root cause? Network latency amplified by chatty JSON payloads between services that needed to exchange complex data structures dozens of times per request. They had fallen into the same …
Continue reading gRPC: The Communication Protocol Your Microservices Actually Need